
I feel like this security questionnaire is trolling me.
Q: Are AS/400s used to process, store data or used for scoped services?
A: We are not a hat factory in 1993.
I feel like this security questionnaire is trolling me.
Q: Are AS/400s used to process, store data or used for scoped services?
A: We are not a hat factory in 1993.
To log into the Teams website on my Mac:
Security engineering in the movies: Fighting off attackers with a katana.
Security engineering in real life: It’s time to draft the Annual Review of Operations Security Policy Report.
“Why isn’t the travel router working?”
“Why is my phone draining, instead of charging?”
Signs that my genius self managed to plug the router into my phone, and the USB charger into itself. Fortunately, straightening all the cables got everything working again with no blown fuses.
Current status:
“Hi $vendor, I confess that I’ve never seen a vendor explicitly state that their encryption-at-rest policy doesn’t cover servers. That’s a new one.”
For reasons, we use a sales tool called Apollo at work. To use it, your employees have to sign into a few of the scammiest websites anywhere, with fake privacy policies and Google App configs that scream “send my email to North Korea”.
That’s gross incompetence and I’m doing what I can to push us to find a better vendor.
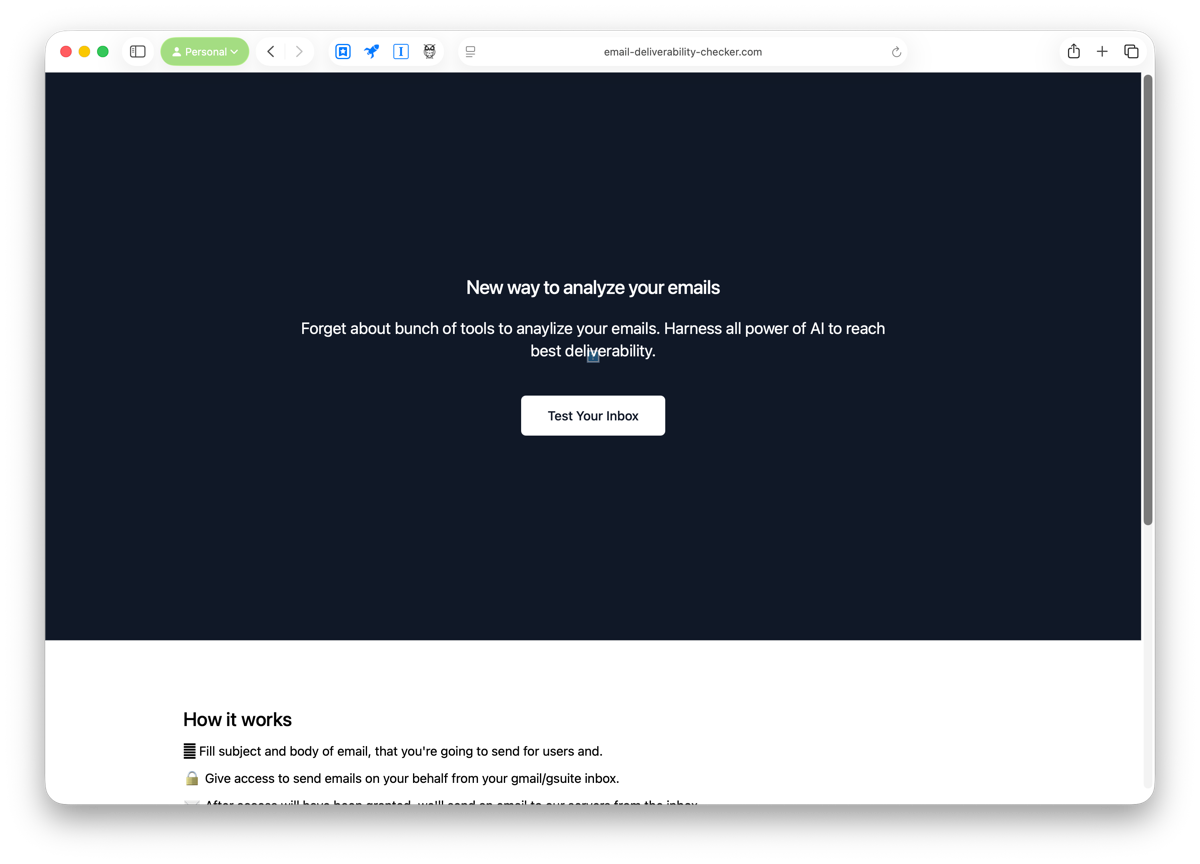
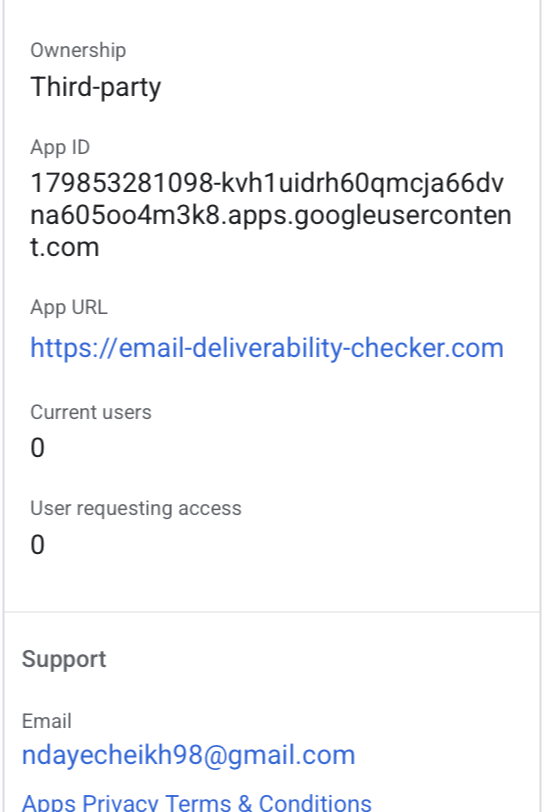
I’ve never seen a vendor brave enough to make this claim.

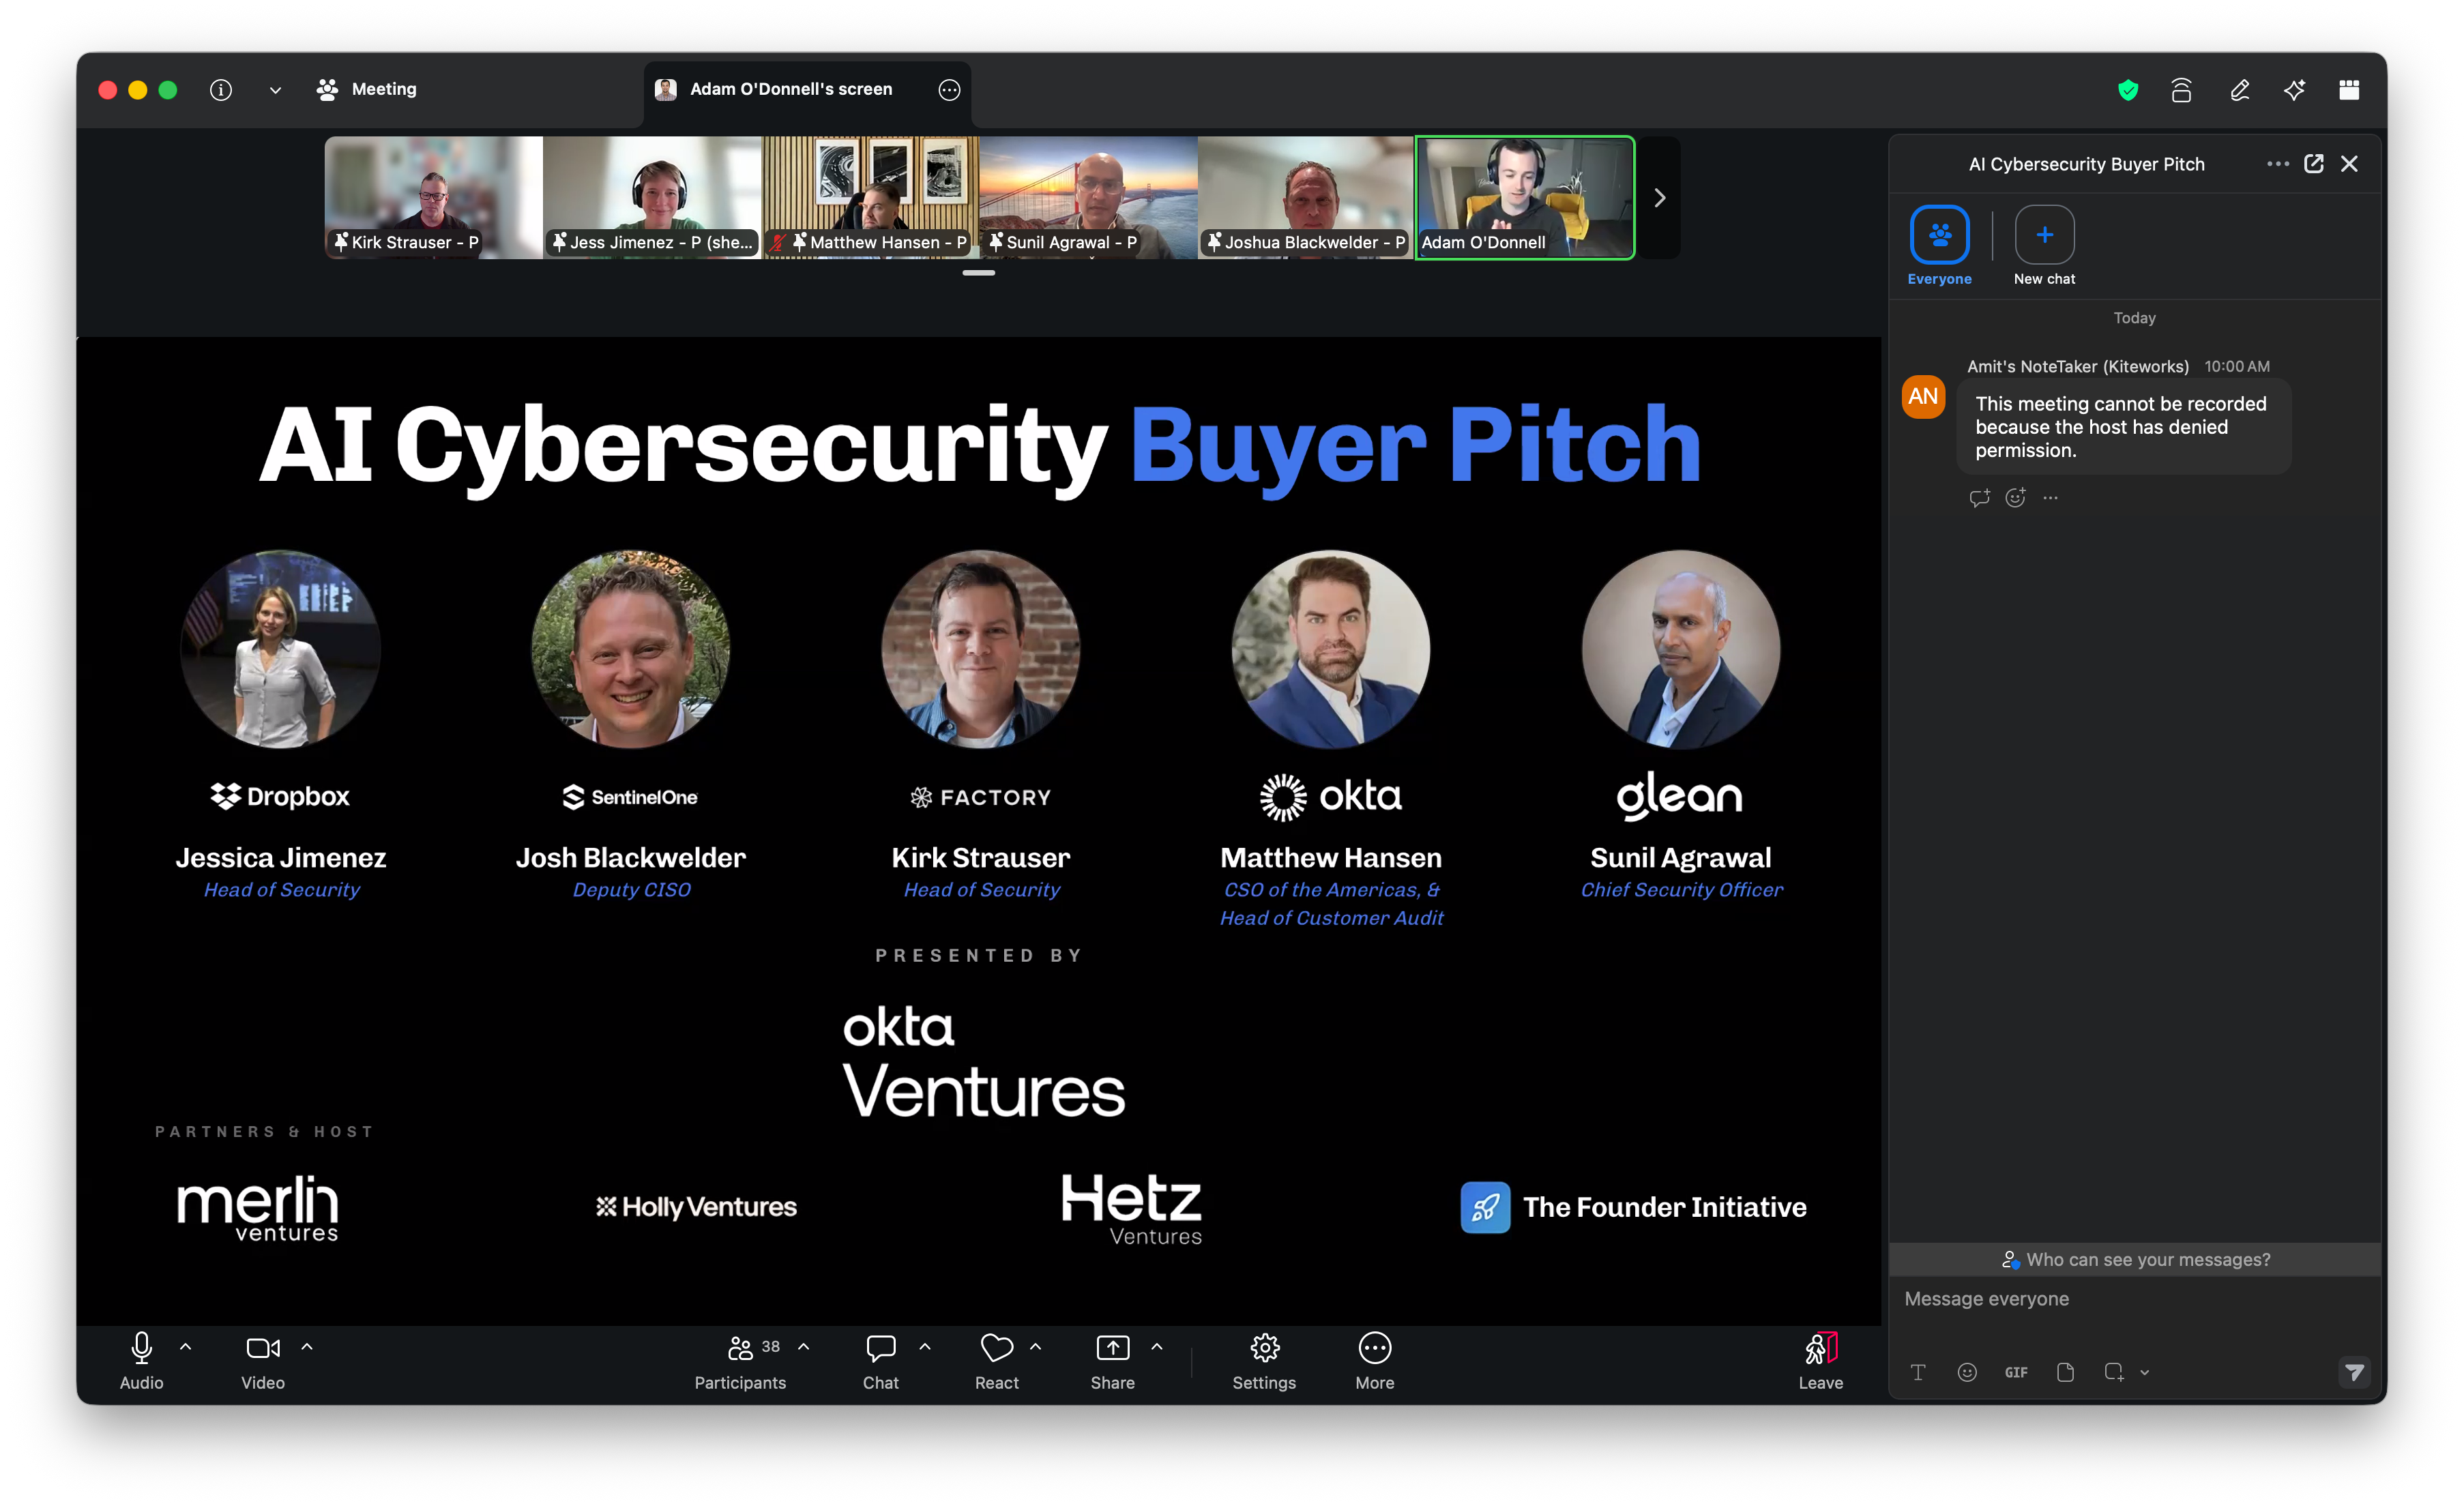
I get invited to the most unexpected events. The more astonished I am that someone would want me at a thing, the more likely I am to accept. That’s how you open the tap to being invited to even more things later. Practice saying yes when you can.
I logged into one of our vendors for the first time to make some urgent changes. Every third time I tried to click on something, instead of going to that thing, I got an obnoxious full-screen onboarding screen with no way to close it:
If I hit my browser’s back button, half the time I got a “submit this form again?” popup.
If you really want to thank me because you really value me as a customer, please stop asking me stupid questions and let me use the site I logged into.
That feeling when you get to the point where can tell what a company’s compliance regime is going to be like based on the layout of their trust center. “Oh, standard Vanta format. It’s probably fine.”
And then you realize that this is not an S-tier superpower.